Longhorn 是 Kubernetes 的云原生分布式块存储。
Install
注意:在安装 longhorn 之前,需要先在节点上安装 iSCSI:
1 | yum install -y iscsi-initiator-utils targetcli |
然后安装 longhorn:
1 | helm repo add longhorn https://charts.longhorn.io |
Longhorn 是 Kubernetes 的云原生分布式块存储。
注意:在安装 longhorn 之前,需要先在节点上安装 iSCSI:
1 | yum install -y iscsi-initiator-utils targetcli |
然后安装 longhorn:
1 | helm repo add longhorn https://charts.longhorn.io |
借助 template 插件可以实现泛域名解析,语法如下:
1 | template CLASS TYPE [ZONE...] { |
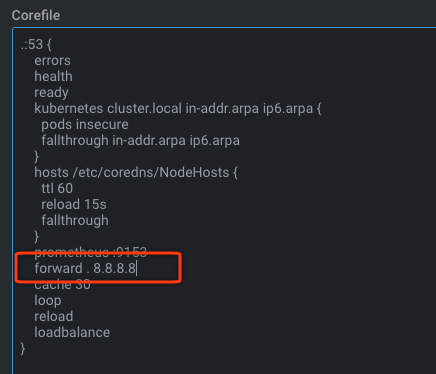
1 | .:53 { |
References
httpbin 是一个 HTTP Request & Response Service,你可以向他发送请求,然后他会按照指定的规则将你的请求返回。
1 | apiVersion: apps/v1 |
cert-manager 是一个云原生证书管理开源项目,用于在 Kubernetes 集群中提供 HTTPS 证书并自动续期,支持 Let’s Encrypt / HashiCorp / Vault 这些免费证书的签发。
1 | helm install cert-manager jetstack/cert-manager \ |
安装时必须设置installCRDs=true,否则后面安装Issuer会抛出下面错误:
error: no matches for kind “Issuer” in version “cert-manager.io/v1”
本文的目标便是将图片转成 .ico 图标。
支持图片格式:
pngjpgjpeg依赖:
sips:macOS 系统自带的图片处理工具imagemagick:一套开源的、强大且稳定的图片处理工具包,需提前安装 brew install imagemagick思路:
sips 命令得到图片的宽度sips 命令生成 iconseticonutil 命令将 iconset 转换成 icns 文件convert 命令将 icns 文件转换成 ico 文件关于如何搭建k3s集群,可以参考我的上一篇文章,本文介绍如何在k3s集群中开启firewall。
下面是一些常用的端口:
| PROTOCOL | PORT | DESCRIPTION |
|---|---|---|
| TCP | 2376 | Node driver Docker daemon TLS port |
| TCP | 2379 | Etcd client requests |
| TCP | 2380 | Etcd peer communication |
| TCP | 6443 | Kubernetes API |
| UDP | 8472 | Canal/Flannel VXLAN overlay networking |
| TCP | 9099 | Canal/Flannel livenessProbe/readinessProbe |
| TCP | 10250 | Kubelet API |
| TCP | 10254 | Ingress controller livenessProbe/readinessProbe |
| TCP / UDP | 30000-32767 | NodePort port range |
Error: Kubernetes cluster unreachable: Get “http://localhost:8080/version?timeout=32s": dial tcp [::1]:8080: connect: connection refused
报错原因:
helm v3版本不再需要Tiller,而是直接访问ApiServer来与k8s交互,通过环境变量KUBECONFIG来读取存有ApiServre的地址与token的配置文件地址,默认地址为~/.kube/config。
解决办法:
KUBECONFIG来解决这个问题:export KUBECONFIG=/etc/rancher/k3s/k3s.yaml。ln -s /etc/rancher/k3s/k3s.yaml ~/.kube/config。k3s是经CNCF一致性认证的Kubernetes发行版,专为物联网及边缘计算设计。
| 服务器 | 用途 | 配置 | IP |
|---|---|---|---|
| k3s-master | k3s-server(master节点) | 2C2G | 10.17.56.20 |
| k3s-agent1 | k3s-agent(agent节点1) | 2C2G | 10.17.56.21 |
| k3s-agent2 | k3s-agent(agent节点2) | 2C2G | 10.17.56.22 |
这三台机器安装的是CentOS7系统。
1 | version: 0.1 |
1 | version: '3.7' |
使用docker-compose up -d命令启动代理服务。